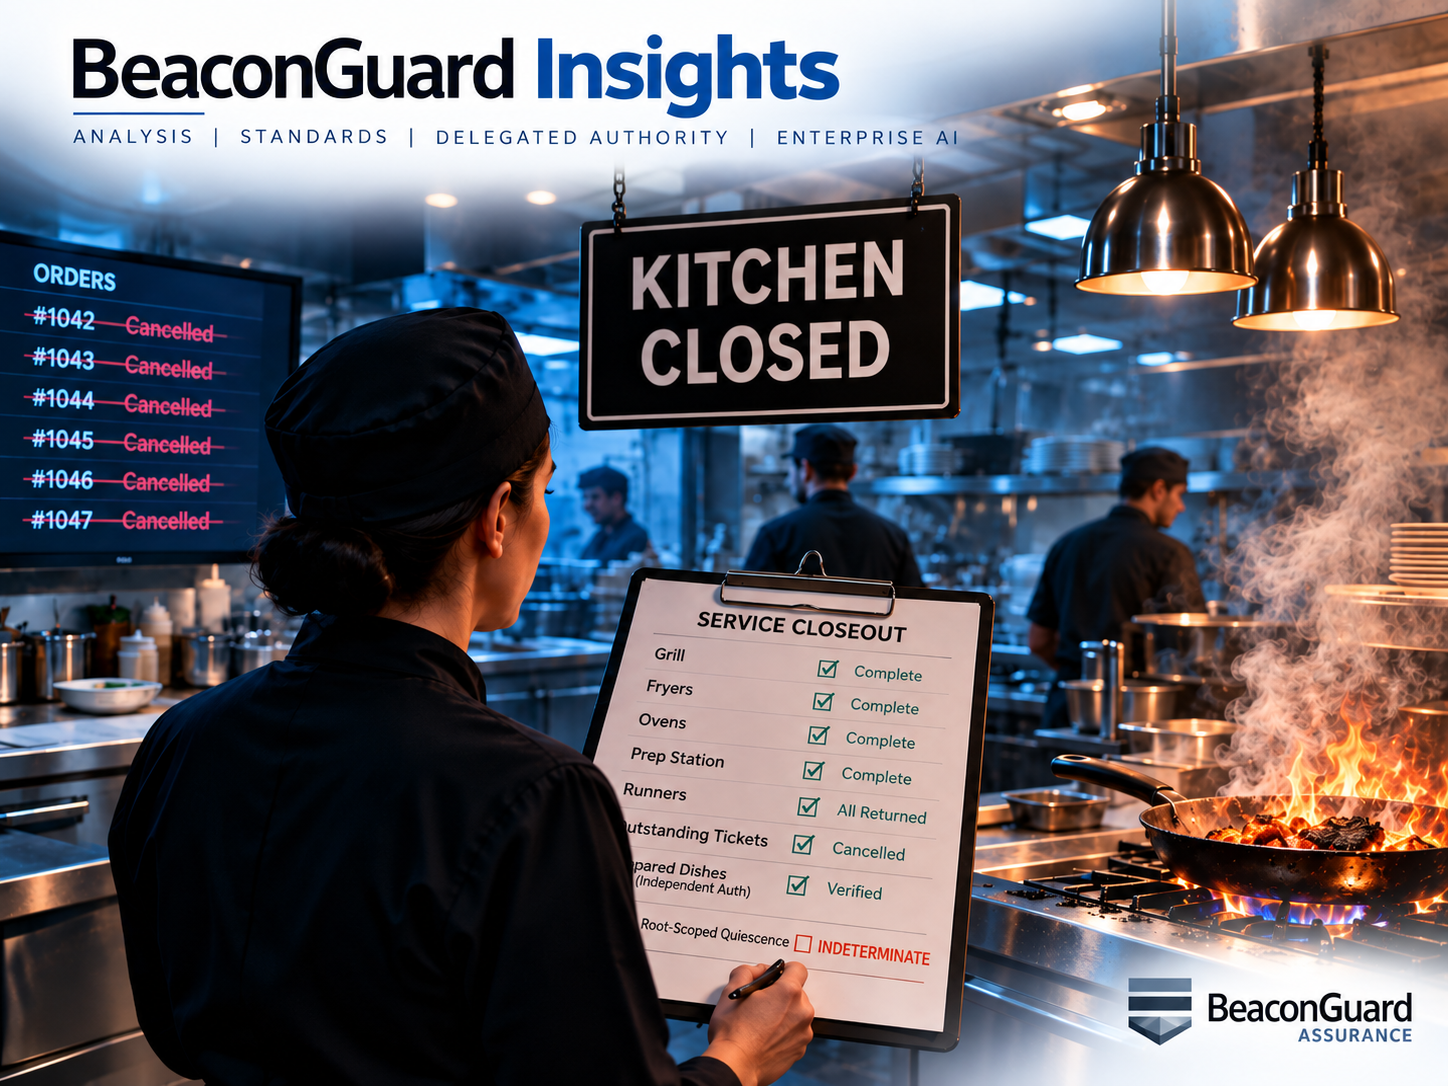
Cancellation ends a request. Quiescence proves an authority path is closed.
A shutdown command and proof of shutdown are different assurance objects.
Long-running AI workflows introduce a question that traditional application controls were not designed to answer:
When an authorization is withdrawn, revoked, or cancelled, what evidence proves that the retired authority can no longer produce a consequential effect?
A cancellation request is a control transition. A credential revocation is a control transition. A workflow stop signal is a control transition.
They may all be necessary.
But in distributed AI systems, the assurance question is different:
Has every remaining path that could allow the retired authorization to create a future protected effect been closed, or has the system lost enough visibility that the answer is unknown?
This distinction matters as AI systems become more autonomous, distributed, and capable of delegating work across multiple services.
The question is not whether a system received a stop command.
The question is whether the system can produce evidence that the authority behind future execution has actually ended.
A different decision object
Research by Zhu and Wang introduces the concept of root-scoped authorization quiescence for long-running AI agent workflows.
The paper examines a specific assurance problem:
A user or system authority initiates work. That authority is later retired. Some work may already have been delegated, queued, reserved, or distributed across multiple execution paths.
The remaining question is not:
"Was cancellation requested?"
The question is:
"Can this retired authorization root still cause a future protected effect?"
The authors propose a protocol architecture involving concepts such as:
- durable authorization cuts;
- sink fences;
- support accounting;
- channel-token tracking;
- atomic rebind;
- and signed evidence certificates.
These mechanisms are one proposed architecture for proving root-scoped quiescence. They should not be interpreted as a universal requirement for every AI system.
Simpler systems may establish sufficient closure through simpler mechanisms when they can demonstrate complete mediation, complete coverage, and reliable evidence.
The broader architectural lesson is independent of any specific implementation:
A shutdown command and proof of shutdown are different assurance objects.
The difference between cancellation and quiescence
In many systems today, cancellation semantics are intentionally limited.
A request to cancel work may mean:
- stop future scheduling;
- request cooperative termination;
- invalidate a credential;
- prevent new operations;
- or notify downstream components.
Those controls can be valuable.
However, they do not automatically prove that every previously issued authority path has stopped.
Distributed AI workflows complicate this further because authority can exist in multiple forms:
- delegated tasks;
- queued actions;
- service credentials;
- provider-side execution state;
- callbacks;
- asynchronous jobs;
- external integrations.
A system may successfully process a cancellation request while still lacking evidence that every relevant execution path has closed.
The assurance boundary therefore moves from:
"Did we issue the stop?"
to:
"Can we demonstrate that the retired authority cannot continue producing protected effects?"
The CAPABILITY of a control is not the same as evidence of closure
The distinction is important because different controls answer different questions.
Credential revocation can answer:
"Is this credential still accepted?"
A workflow cancellation can answer:
"Was this workflow asked to stop?"
A provider shutdown mechanism can answer:
"Did this provider stop this execution path?"
None of those automatically answer:
"Are all paths derived from this retired authority unable to create future protected effects?"
That final question requires a defined scope, evidence model, and decision boundary.
Three possible outcomes: quiescent, not quiescent, or unknown
One of the most important ideas in the paper is treating uncertainty as a real state.
A shutdown evaluation should not be forced into a binary answer when evidence is incomplete.
A root-scoped evaluation can result in:
QUIESCENT
Evidence supports that the retired authority root no longer has a path to produce a protected effect within the declared boundary.
NOT QUIESCENT
Evidence shows that a remaining path can still produce a protected effect.
INDETERMINATE
The system cannot establish either outcome because required evidence is missing, stale, incomplete, conflicting, or outside the observable boundary.
For high-consequence AI workflows, this third state is important.
Unknown is not equivalent to stopped.
Figure 1 — A cancellation or revocation event is a control transition. Quiescence is an evidence-backed determination — incomplete evidence is indeterminate, not success.
The paper's proposed architecture
Zhu and Wang's work describes a formal architecture intended to establish quiescence under stated assumptions.
The model includes:
Durable authorization cut
A point after which new effects from a retired authority root should no longer be accepted.
Sink fences
Controls that prevent downstream effect commitments associated with the retired root.
Support accounting
A method for determining which authority roots still support a piece of work.
Atomic rebind
A mechanism for preserving work that remains independently authorized while removing dependence on the retired root.
This final point is important.
A safe shutdown model is not necessarily "terminate everything."
Consider a delegated task supported by two independent authorization roots. Removing one root should not automatically invalidate work that remains legitimately supported by another.
The assurance objective is not destruction of activity.
It is accurate authority accounting.
Assumptions matter: proving closure requires visibility
The paper's results depend on explicit assumptions.
Among the stated requirements are:
- complete authorization-root coverage;
- accurate manifest completeness;
- reliable sink-fence enforcement;
- exact channel accounting;
- authentic evidence;
- durable state transitions;
- atomic rebind behavior;
- crash-safe monotonic state handling;
- eventual evidence stabilization for convergence.
These assumptions are significant.
A system cannot prove that authority has disappeared if it cannot enumerate where that authority may still exist.
Missing visibility does not become success.
It becomes indeterminate.
This is a broader lesson for enterprise AI systems:
The quality of an authorization decision depends not only on policy rules, but also on whether the system can observe and prove the state those rules depend on.
What the evaluation results show — and what they do not
The authors report evaluation results for their implementation and test harness.
Reported results include:
- a provider-free late-effect test suite with 17 registered outcomes;
- checker validation of 17/17 traces;
- rejection of 44/44 semantic regressions.
These are author-reported results from the paper's evaluation artifacts.
They demonstrate the behavior of the authors' implementation and testing approach under the described scenarios.
They do not establish:
- production deployment success;
- universal effectiveness across AI platforms;
- independent reproduction;
- adoption by standards bodies;
- or validation by BeaconGuard.
Independent validation of the protocol remains unknown due to the recency of the work.
Existing protocols and the shutdown question
Current ecosystem protocols often provide cancellation or revocation primitives.
For example:
- MCP task semantics describe cancellation as a cooperative operation rather than guaranteed immediate termination.
- Agent communication systems may provide task lifecycle controls.
- OAuth token revocation provides a mechanism for invalidating credentials.
These mechanisms solve important problems.
They do not necessarily attempt to prove root-scoped effect closure.
That is a different decision object.
The distinction is not that existing controls are insufficient.
The distinction is that they answer different questions.
Where this fits in enterprise AI authorization
Enterprise AI authorization is moving beyond initial approval.
Organizations increasingly need answers across the lifecycle:
- Who initiated this action?
- What authority allowed it?
- Was that authority still valid?
- Was delegated work still within scope?
- What happened when authority changed?
- Can we prove that retired authority stopped producing effects?
This creates several related assurance dimensions:
Identity
Who is acting?
Authority
What actions are allowed?
Delegation
What authority was transferred and how far?
Lifecycle
What happens when authority changes?
Closure
Can the organization prove that retired authority no longer has execution impact?
Root-scoped quiescence addresses the final dimension.
How this relates to BeaconGuard
BeaconGuard uses the term continuous authorization assurance to describe the broader category of evaluating consequential AI actions against current authority, policy, and evidence conditions.
The Zhu/Wang paper is not a BeaconGuard implementation, validation, or endorsement.
BeaconGuard does not claim to implement the paper's protocol mechanisms.
The relevance is architectural:
Authorization assurance does not end when authority is granted.
Organizations operating consequential AI workflows also need confidence that authority transitions, delegation changes, and shutdown events produce verifiable outcomes.
Questions enterprise teams should ask
Before relying on cancellation or revocation controls for autonomous workflows:
- What exactly does cancellation guarantee?
- Which execution paths can retain authority after cancellation?
- Can delegated work continue under another valid authority?
- What evidence proves a retired authority root is no longer effective?
- What happens when a provider cannot provide closure evidence?
- Does missing evidence produce a safe unknown state, or an assumed success?
These questions become more important as AI workflows become longer-lived and more distributed.
Start with one consequential workflow
Organizations do not need to solve every AI shutdown scenario at once.
- identify the authorization boundary;
- identify where delegated execution occurs;
- identify what evidence exists when authority changes;
- determine whether shutdown means a request was sent or a state can be proven.
The goal is not simply stopping an AI workflow.
The goal is knowing what authority remains, what authority ended, and what evidence supports that conclusion.
# Source Notes and Claim Tiers
Tier 1 — Primary source
Zhu and Wang, "Root-Scoped Authorization Quiescence for Long-Running AI Agent Workflows," arXiv:2609.21284
Used for:
- definition of root-scoped authorization quiescence;
- proposed protocol architecture;
- formal assumptions;
- three-valued decision model;
- author-reported evaluation results;
- scope limitations.
Claim classification:
FACT ABOUT THE PAPER / AUTHOR-DOCUMENTED DESIGN
Tier 2 — Author-reported evaluation
Claims:
- 17/17 registered outcomes;
- checker validation;
- 44/44 semantic regression rejection.
Classification:
AUTHOR-REPORTED RESULTS
Not independently verified.
Tier 3 — Protocol ecosystem context
Sources:
- MCP task lifecycle documentation.
- Agent communication lifecycle documentation.
- RFC 7009 OAuth token revocation.
Used for:
- cancellation semantics;
- credential revocation context.
Classification:
PRIMARY PROTOCOL FACTS
Interpretation that these mechanisms answer a different decision object is:
BeaconGuard editorial analysis.
Claim boundaries
This article does not claim:
- Zhu/Wang's protocol is a universal requirement.
- Existing cancellation mechanisms are defective.
- MCP or A2A systems are non-quiescent in production.
- OAuth revocation is inadequate.
- BeaconGuard implements the paper's architecture.
- The paper validates BeaconGuard.
- The paper represents an adopted standard.
Editorial thesis
A cancellation request changes control state.
A quiescence determination requires evidence that retired authority can no longer produce protected effects within a defined scope.
When evidence is incomplete, the correct state is not success.
It is indeterminate.